Adversary DNA: we named the botnet
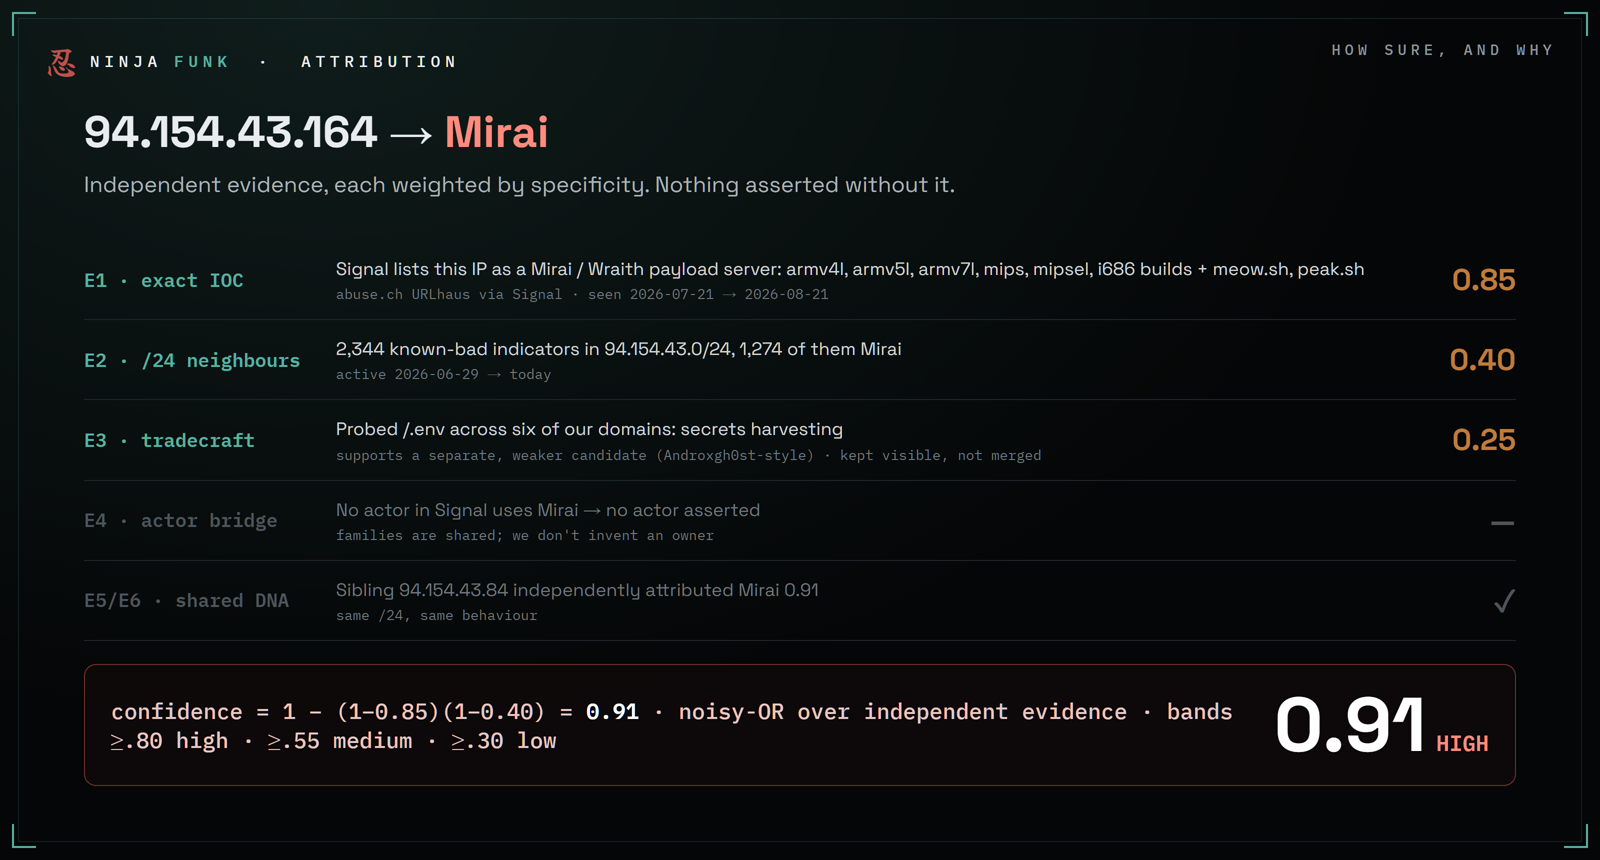
From one suspicious request to a named Mirai botnet at 0.91 confidence, with the evidence chain and an incident Claude triages on its own.
Direct attributionLocal sensor93 s
Local sensors fingerprint hostile traffic where your logs live. Our attribution engine names the botnet behind it, with a confidence score and the evidence to check it. CHATTER reads eleven live threat feeds so your team doesn't have to.
Both recorded end to end in 4K on the live platform on 24 September 2026. What you see is what the lab saw.
A reputation lookup gives you a verdict. Our attribution engine gives you a name, a confidence score and the evidence behind it. Independent evidence is combined, and nothing is asserted without it. If the graph can't prove an actor, it names none.
An isolated, off-production stack with its own graph. It reads the estate. It never writes to it.
Analysis runs on the host that owns the logs. Only findings ship; raw logs never leave the box.
LiveA behavioural fingerprint per hostile source. The same DNA from new IPs exposes operators rotating addresses.
LiveBotnet, campaign and actor, each with a confidence score, a band and a checkable evidence chain.
NewEleven live feeds embedded on the box, linked to the nearest known threat, scored for novelty, read into a forecast.
LiveAsk the threat graph in plain language. Answers are cited to graph nodes, and refused when the graph has nothing.
ExperimentalLink prediction over research graphs: where two fields are about to collide, with the backtest published.
Experimental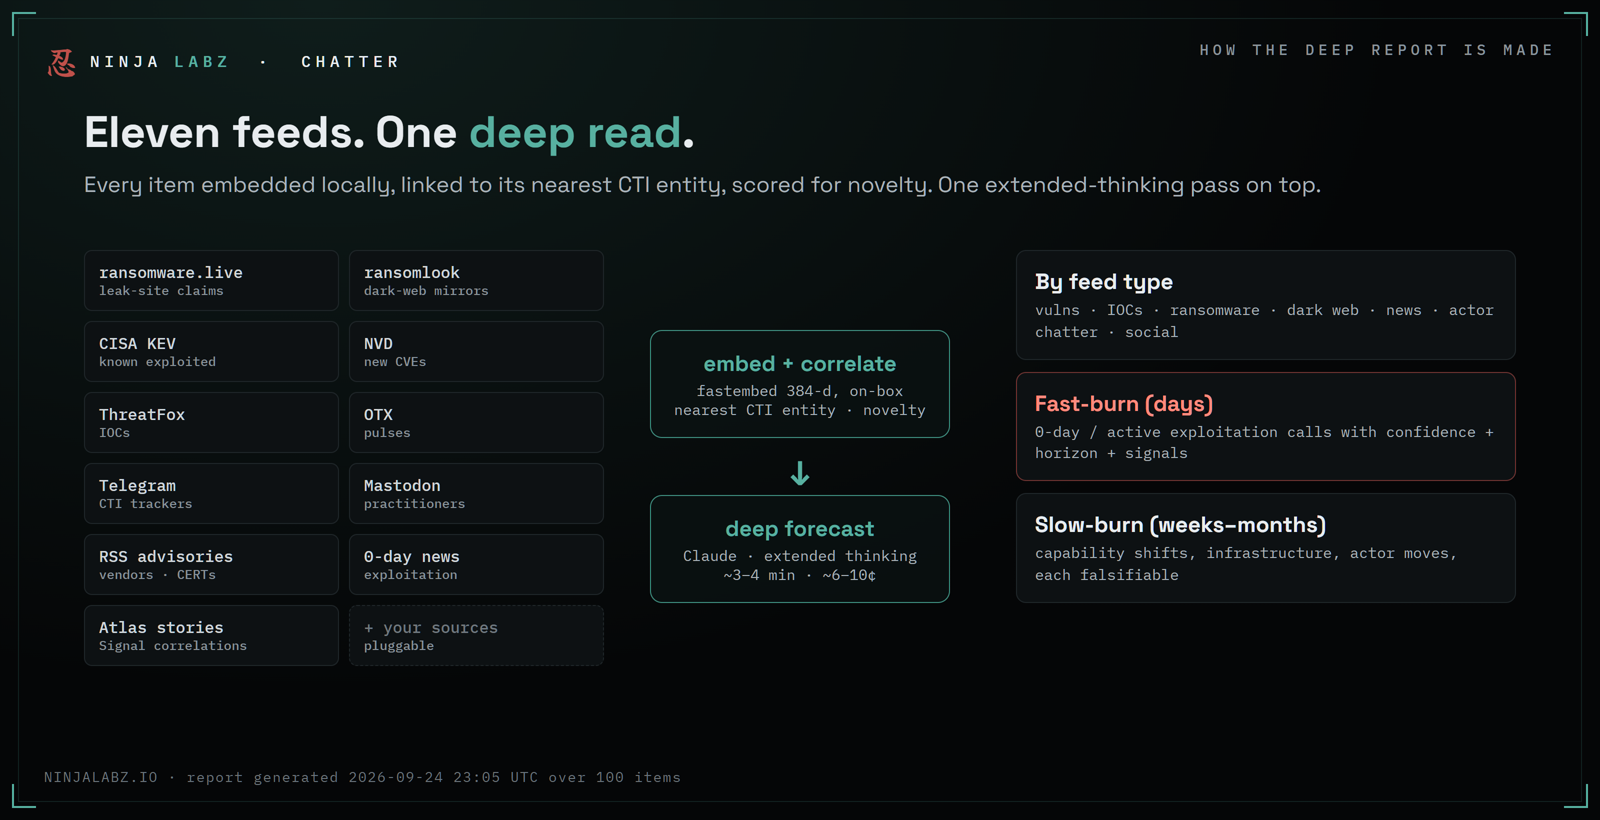
Sensors fingerprint locally. Only findings, and the IPs you choose to check, leave the host.
Every attribution carries its chain. Every confidence has a formula you can recompute.
Forecasts carry a window and get graded in public. Last edition: one hit, one miss, one unverified.
Its own network and graph. Experiments can break here without touching anything live.
We're opening the lab to a small group of design partners: security teams with a web edge, a SOC and a preference for evidence. You keep your logs. We bring the sensor, the threat intel and the attribution engine.